概述
产品型号:WL-WN530BE1-A
固件版本:M30BE1_V251117
漏洞类型:未授权远程命令注入及栈溢出
漏洞描述:WAVLINK WL-WN530BE1-A 是面向家用和小型办公场景的 BE3600 Wi-Fi 7 路由器,本次分析固件为
M30BE1_V251117。该型号上目前有三条已公开的未授权漏洞:两条位于 ioos后端的命令注入(CVE-2026-120198、CVE-2026-113802),以及一条位于 /cgi-bin/ExportAllSettings.cgi的栈溢出(CVE-2026-109109)。其中 CVE-2026-120198 与 CVE-2026-109109 的 CVSS 3.1 均为 10.0。
固件下载 :https://docs.wavlink.xyz/Firmware/?category=Router&model=WL-WN530BE1-A
系统模拟
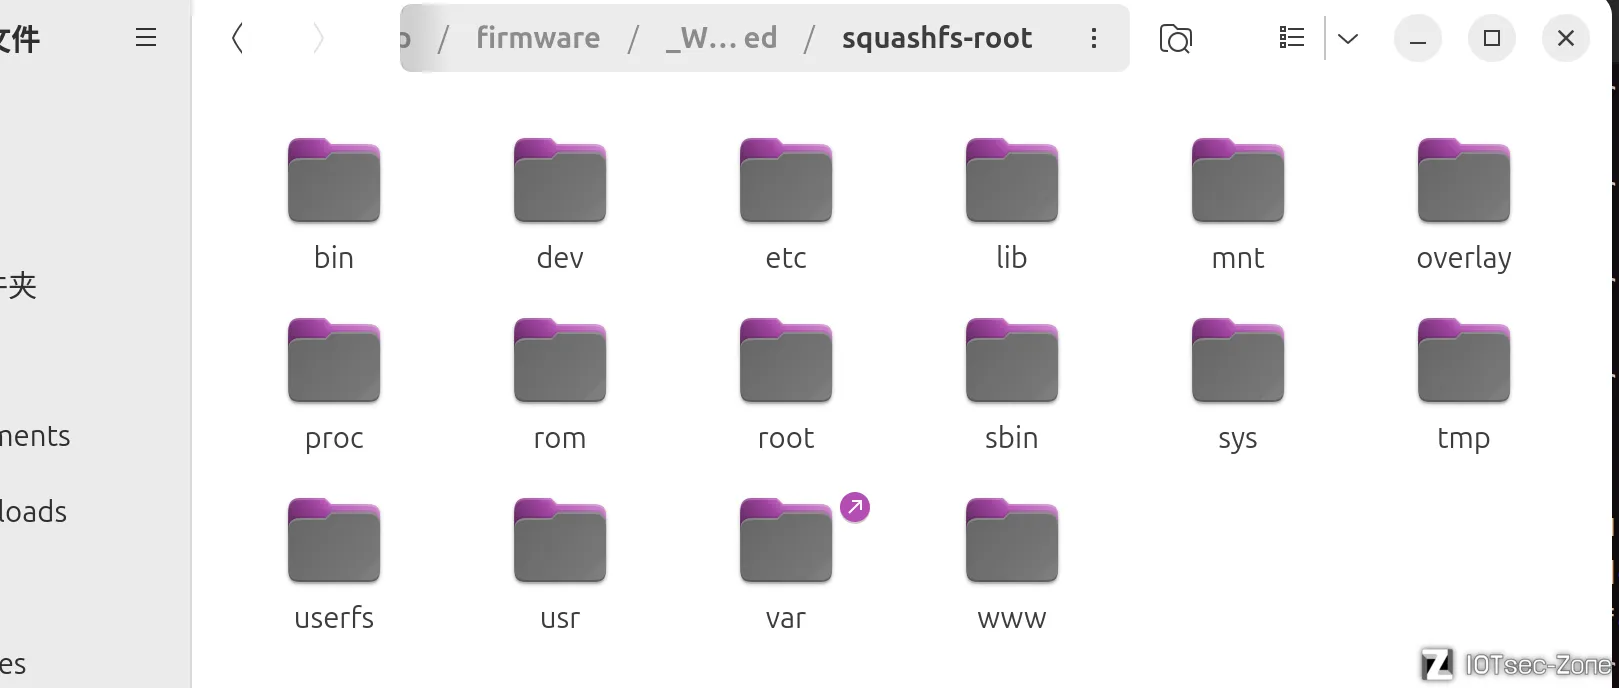
binwalk解包
binwalk -Me WN530BE1_WAVLINK-WO-2025-11-17-8fdfa208c7_tclinux.bin
checksec ./bin/busybox
🍻 squashfs-root checksec ./bin/busybox
[*] '/home/pipi/Desktop/firmware/_WN530BE1_WAVLINK-WO-2025-11-17-8fdfa208c7_tclinux.bin.extracted/squashfs-root/bin/busybox'
    Arch:       arm-32-little
    RELRO:      Full RELRO
    Stack:      Canary found
    NX:         NX enabled
    PIE:        No PIE (0x10000)
🍻 squashfs-root
ARM32小端序,开启了Canary及NX保护
模拟流程
#qemu系统模拟
#- Debian 12 arm64 内核 6.1.0-51-arm64:CONFIG_COMPAT=y、CONFIG_COMPAT_32BIT_TIME=y
#- QEMU cortex-a53 支持 AArch32 EL0
qemu-system-aarch64 \
    -m 2048 \
    -cpu cortex-a53 \
    -M virt,virtualization=true \
    -nographic \
    -drive if=none,file=debian-12-nocloud-arm64.qcow2,format=qcow2,id=hd0 \
    -device virtio-blk-device,drive=hd0 \
    -netdev tap,id=net0,ifname=tap0,script=no,downscript=no \
    -device virtio-net-device,netdev=net0 \
    -bios /usr/share/qemu-efi-aarch64/QEMU_EFI.fd

#宿主机ip配置
sudo tunctl -t tap0 -u `whoami`
sudo ifconfig tap0 192.168.10.1/24 up

#aarch64虚拟机ip配置
ip link add br0 type dummy
ifconfig eth0 192.168.10.2/24
ifconfig br0 192.168.10.3/24

#宿主机压缩并传输文件
tar -cvf web.tar.gz squashfs-root/
python3 -m http.server

#aarch64虚拟机
wget http://192.168.10


